HEX DEREF X - (Endpoint Security | Anti-malware) - Advanced proactive and Next-Generation Antivirus (NGAV) in one unified solution with Zero Trust architecture at the application/process level (allowlisting) seamlessly integrated with malware analysis


Source code
Investors
Case study
Zero trust
Advanced application control
Malware analysis
The superficial protection offered by traditional antivirus solutions
Advanced kernel-level memory scanner
Key features
Code-signed malware
HEX DEREF X is a standalone, proactive Windows endpoint security solution that fills the blind spots left by conventional antivirus with offline-capable Defender for Endpoint-style visibility and protection. Protect your devices (workstations, laptops, virtual machines and Windows servers) in a whole new way. Nothing runs without the user's knowledge. The product combines the capabilities of multiple high-end analysis tools, such as ProcMon64 and System Informer into a single, unified, high-performance solution operating at the kernel level. These capabilities have been implemented as a proprietary, lightweight, and fully integrated platform, making the product a technically distinctive solution in the endpoint security market.
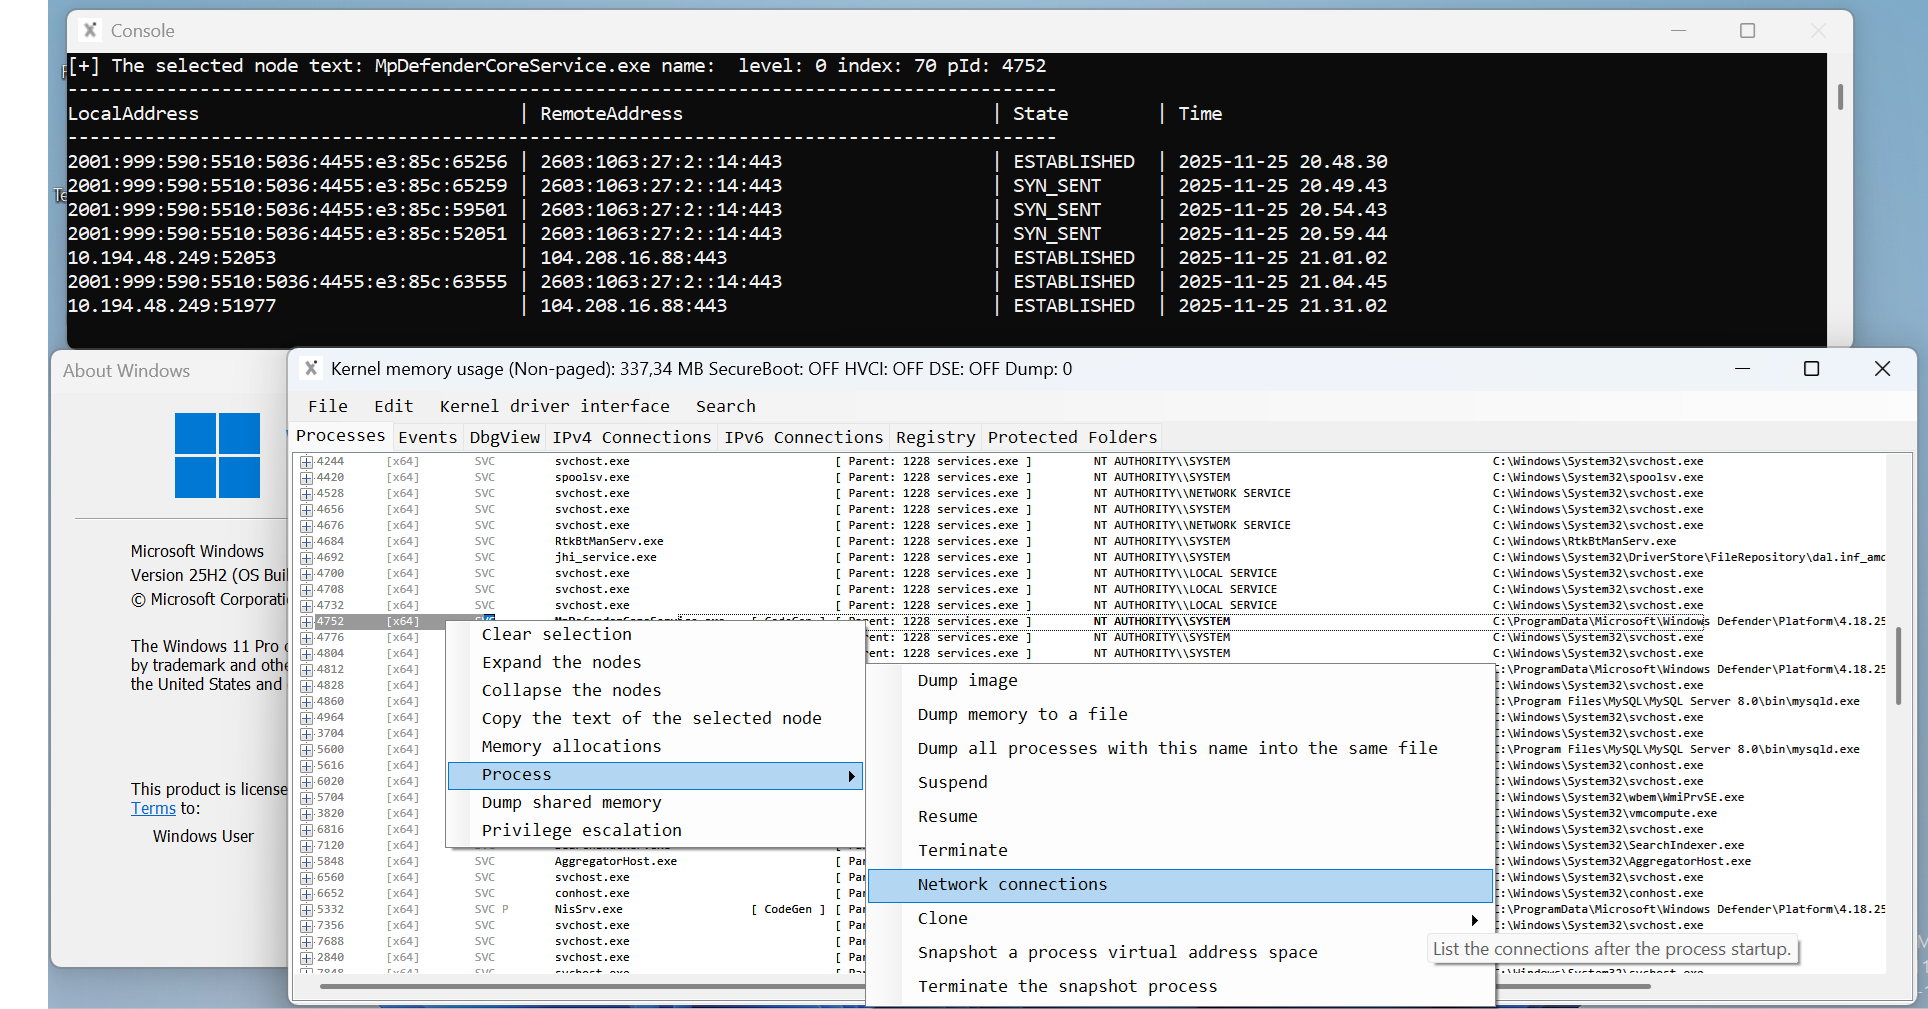
Full size HEX DEREF ANTI-MALWARE X - Process network connections are saved into the database
A somewhat new approach: not merely reacting to threats, but nullifying their impact before they even activate. Even a state-sponsored cyberattack is intercepted and stopped in real-time at the first compromised endpoint in this implementation's Zero Trust mode. This solution not only block malware. It renders malwares irrelevant. And has been specifically developed to assist malware analysts and enhance the operational capabilities of Security Operations Centers (SOC) across TIER 1 to TIER 3 levels.

Currently supported versions: Windows 10 22H2 - Windows 11 25H2 (x64)

Full size HEX DEREF_ANTI-MALWARE_X
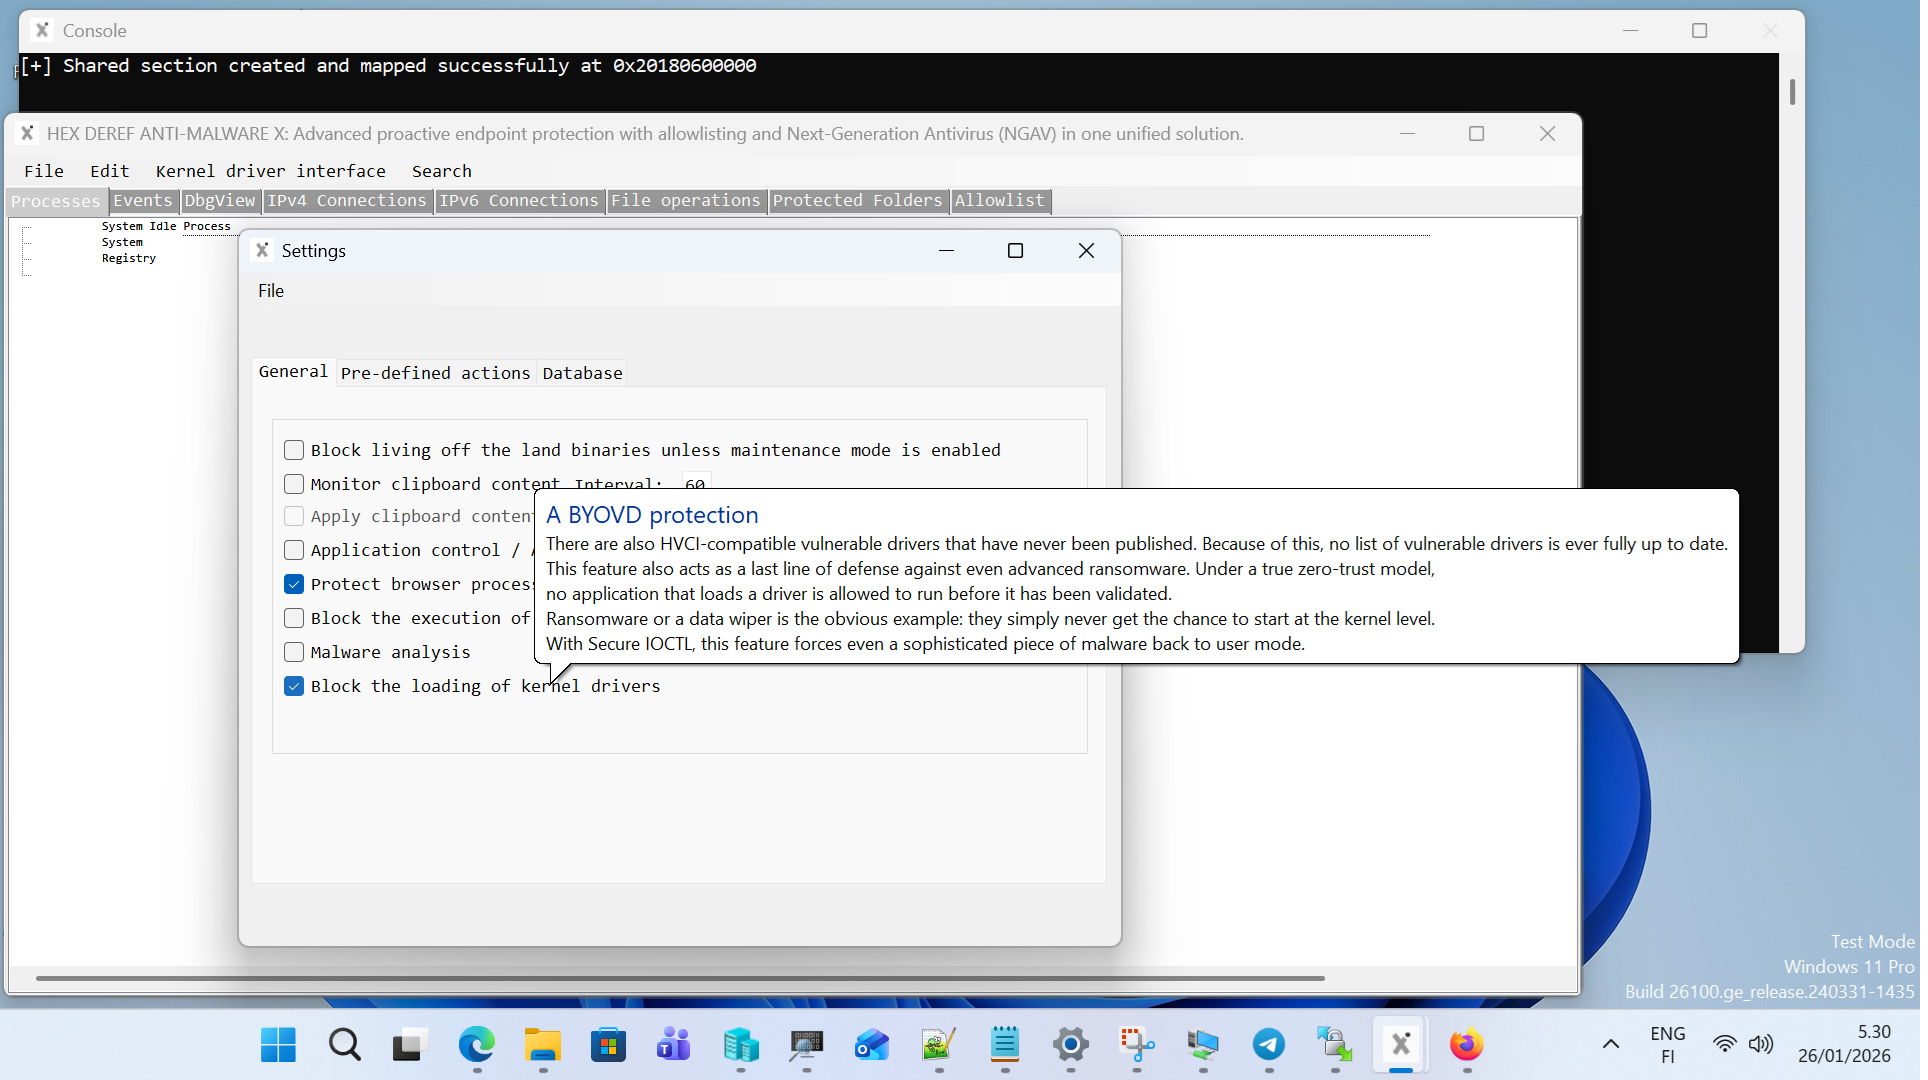
Malware may be deployed through remote access using credentials exposed in a breach, insider-launched malware, an undisclosed 0-day vulnerability (CVE-2025-53770), or triggered accidentally by an employee without malicious intent.

When a ransomware attack is launched, endpoint security that cannot respond to these attacks in real time is, in this situation, is about as useful as having no protection at all. A malware backed by a state actor will, of course, reboot the device, effectively rendering the efforts of the cyberattack investigation team arriving on site almost entirely useless. Detection-based security does not recognize nor protect against unknowns, including new malware. Unknowns are only discovered and addressed by legacy detection-response (EDR) endpoint security providers once it has done damage to their clients.

Full size HEX DEREF_ANTI-MALWARE_X
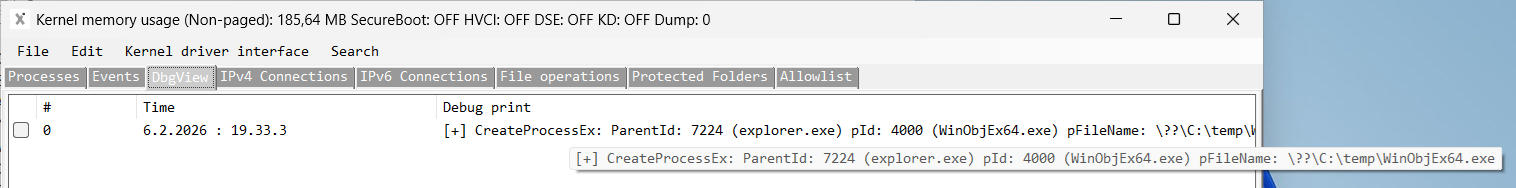
Should the threat actor’s mission be to discreetly extract all data valuable for industrial espionage, the applications will not execute due to being absent from the allowlist. This action instantly generates a real-time alert, and the device is immediately isolated from the network as a precautionary measure.

This kind of malware deletes the logs and then renders the device unbootable. In such a situation, the only effective solution is the zero-trust mode. That means no unknown code — including digitally signed code — is executed within the company until a designated person has tested and verified it as safe.

By intercepting all unknown code at the kernel level in real time, these attack vectors are neutralized — eliminating both risk and reputational damage. This approach is particularly suited for small businesses (SMBs) lacking the budget for comprehensive round-the-clock SOC services.

Additional features includes advanced malware analysis and memory forensics. In malware analysis mode, hardly any threat goes undetected. This implementation corners the malware in its analysis mode and forces it to reveal itself. The anomaly detection feature preemptively blocks the execution of the process and flags it for manual analysis. As proactive measures, it can capture a real-time memory dump from both kernel and user space.

If your organization mostly uses Microsoft software or just a few other sofwares. This is the perfect solution. Simplicity is key. Nothing runs without an approval. The designated person or team adds them to the allowed list in Zero Trust mode. With the Home Edition, you stay in control — only the programs you approve can run. Nothing happens behind your back, ensuring complete transparency and peace of mind.

Proactivity refers to the ability to respond when an anomaly is detected on a device. In the example case, unknown code is executed on a device — code that has never previously run on any company system. The solution then performs a predefined action. For instance, as a precautionary measure, take a memory dump from the device or isolate it from the network.

Real-time threat prevention in code-signed malware that exploits previously undisclosed zero-day vulnerabilities

Malware signed with a legitimate and valid code signing certificate poses a unique challenge because it can appear trustworthy to endpoint protection systems. These threats must not be allowed to execute until they are explicitly verified as safe. In practice, only a zero-trust mode can block such state-sponsored threats in real time. Zero-trust architecture treats all code — even signed — as untrusted until proven safe. HEX DEREF X adds a critical layer of proactivity by checking whether the same code is running on any other device within the organization. This cross-device awareness helps detect lateral movement and coordinated attacks. It enables early containment before malware spreads across the network. The solution doesn’t rely solely on signature validation — it monitors behavior and presence. Zero-day vulnerabilities are flaws unknown to the vendor and unpatched at the time of attack.

The superficial protection offered by tradional antivirus solutions

Recruitment process
A brief review of the /r/Malware community highlights the pace at which new malware variants appear.
A new malware variant requires a manual analysis (both static — IDA PRO and dynamic — HEX DEREF X - ANTI-MALWARE) and separate signature to be created (a static detection). Even if security researchers could begin analyzing new malware immediately after it appears, the time required for reverse engineering, behavioral analysis, validation, and signature development means that detection will inevitably lag behind the threat. As a result, the device of an individual user remain exposed during the period between initial compromise and the release of updated detections.
This inevitably raises the question: why pay for these products if Microsoft Defender is already considered sufficient? When a somewhat comparable product is available for free, a commercial product must offer superior technology; otherwise, it has no real value. In a way, the traditional antivirus approach has failed its users by losing sight of its original purpose. Rather than showing users what is actually happening on their systems, many products collect sensitive information in the background without first obtaining the user's explicit consent.
A Next-Generation Antivirus (NGAV) differentiates itself from traditional methods by detecting a previously unseen threats as anomalies, and through behavioral analysis without relying on static signature-based detection.
In addition to the Zero-Trust concept, the solution offers a mode more suitable for home users, where all unknown code (specifically code without a digital signature is automatically blocked unless explicitly approved). This approach proactively eliminates most threats by design and reduces the attack surface.
The authors tests indicate that certain antivirus solutions perform actions without user consent — raising serious questions about trust, transparency, and privacy. When protection is only surface-level and sensitive data is collected regardless of user settings, it's time to re-evaluate what security truly means.
The articles written by malware analysts from a certain antivirus solution were impressive. However, based on my preliminary tests, these features were not actually implemented in the product itself at a practical level. In other words, the articles are solid and the reverse engineers clearly know what they're doing — but why are these capabilities missing from the product being sold? The protection offered by the product is nowhere near the level suggested by the articles.
This is where HEX DEREF X provides a significant advantage. All essential telemetry, process activity, file operations, registry operations, network visibility, and investigation data are consolidated into a single interface, enabling faster and more efficient threat analysis. For organizations requiring specialized workflows or integrations, the source code is also available for licensing, allowing the platform to be customized to meet the specific requirements of a telecommunications provider, enterprise, or government organization.

A new standard: No malware, just verified execution (Zero Trust)

HEX DEREF X's application- and process-level Zero Trust mode prevents data breaches before they even have a chance to begin. Malware simply cannot operate effectively against an implementation at this level, or it is exposed immediately. One of the product's key capabilities is unlimited logging of process command-line activity and network connection telemetry to a local database. Users can disable these features through the settings if desired. The implementation respects user privacy and does not transmit any sensitive information without the user's explicit consent.

That’s why this solution goes further: It doesn’t trust certificates. It trusts processes. Every executable must be explicitly approved by designated personnel. No implicit trust. No shortcuts. No assumptions. This isn’t about chasing signatures or reacting to threats. It’s about prevention by design. The author’s solution doesn’t just block malware — it makes its existence irrelevant. We’re not just talking theory — stolen code-signing certificates from data breaches or acquired under false pretenses are actively being used to sign malware, giving it a false sense of legitimacy. In these cases, even traditional Zero Trust implementations can be bypassed if they rely solely on certificate validation.
In a zero-trust mode, ransomware has virtually no room to operate, as it simply won't run — whether digitally signed or not. An attacker cannot disable real-time protection on the device without being noticed, even if they gain remote access using compromised credentials. When it comes to IsaacWiper malware’s capabilities, even a single second of exposure is too much. That’s why the author solution stops threats instantly — at the kernel level, in real time, 24/7/365, operating in a zero-trust mode. The solution doesn’t replace your SOC — it empowers it. And for small and mid-sized businesses, it’s the most cost-effective protection on the market.
The attack techniques referenced in the accompanying article CVE-2025-8088 have been evaluated against the current implementation of the solution operating in zero-trust mode. Based on the authors analysis, these techniques are ineffective under this configuration. It is important to note that the volume and diversity of potential attack vectors continue to grow, particularly in cases involving undisclosed zero-day vulnerabilities within specific software applications. Such vulnerabilities, when not publicly disclosed, pose a significant challenge to proactive defense mechanisms and require continuous monitoring and adaptive security measures.
Even insider-originated threats trigger immediate scrutiny, and anomaly detection at the endpoint flags any deviation from normal behavior — including non-published zero-day exploits. These capabilities can be tailored as a custom software work to meet your company’s specific needs, thanks to a streamlined configuration model with only a handful of essential settings.

Case study

This simulates a real-life scenario in which an attacker has gained remote access to a company workstation using privileged administrator credentials. The attacker deploys a previously unpublished piece of malware designed for covert data exfiltration. The objective is to steal user credentials, source code, and any other valuable data that can be monetized on the dark web without the company’s awareness.

All malware variants designed to steal #1 steal #2 or wipe or encrypt data were automatically excluded from execution and subjected to manual analysis due to proactive security measures. When the Security Operations Center (SOC) conducted further testing, it quickly became evident that the file was ransomware — despite being digitally signed. This highlights the importance of layered defense and vigilant analysis.

The company emerged from the cyberattack unscathed. There were no disruptions to core operations, no reputational damage, and no need to deploy a CIRT team on-site. Sometimes a simple solution is better.

Advanced Application Control

The software enforces a Zero Trust model at the application and process level (prevention-first). No application is allowed to run unless it is on the allowlist. This helps stop previously unseen threats that exploit undisclosed zero-day vulnerabilities and, at a minimum, makes such attempts visible for investigation.

The original developer’s implementation differs significantly from competitors in one key aspect: depending on the operating mode, either the device user defines which applications are allowed — at the process level or 'globally' based on digital signatures. Execution control is enforced by designated personnel — whether a SOC lead, security architect, malware analyst, or equivalent — who explicitly approve after manual analysis what is allowed to run. Any unrecognized or unauthorized activity is quarantined and subjected to manual analysis. Only after thorough review and validation is it permitted to execute, ensuring that proactive containment is driven by human oversight.

In Zero Trust mode, applications digitally signed by Microsoft are automatically added to the allowlist.

The moment a third party defines trusted applications on behalf of a company, the design has already fundamentally failed. For example, a program signed with a certificate obtained under false pretenses, or a previously approved application that turns malicious. Naturally, the purchasing company or educational institute must have the ability to remove items from the allowlist. If for no other reason, simply because the software may no longer be in use within the organization.

It’s worth noting that processes or DLL's can be added individually to the allowlist or based on the certificate signer.

Malware analysis

One of the most important capabilities is that processes remain visible in the process list together with their command-line arguments and network connection history, even after the process has terminated or the network connection has been closed. This significantly improves visibility into suspicious activity and can help uncover previously undetected attacks, including those leveraging zero-day vulnerabilities. Because all of this information is available within a single interface in malware analysis mode, threat hunters gain a comprehensive view of system activity from one centralized location.

  • Displays all running processes and their network connections
  • Ensures that unauthorized or suspicious software cannot operate undetected
  • Empowers CIRT teams during on-site investigations to instantly identify potential malware or anomalous activity
  • The system lists only newly initiated processes and their corresponding network connections, allowing immediate visibility into potential command-and-control (C2) communications
  • The solution logs all processes along with their command lines and network connections into the database. This supports the investigation of potential data breaches and malware analysis
  • Even without malware analysis mode activated, this solution enables post-incident verification to determine whether your company was exposed to a potential data breach
  • Your malware analysts are as good as the softwares they use

In certain scenarios, a straightforward approach can outperform complex AI-driven solutions.

What can the on-site CIRT team can do if the malware securely removes itself from the device and restarts it? Not much except send the invoice. If this solution is running in a zero-trust mode, you won’t need them anyway, because the attack stops at the first compromised device.

If a cyberattack does occur, and backups have been restored, but the root cause remains unknown at the endpoint level, this kind of cyber threat mitigation solution needs to be deployed on the device in order to determine the root cause. Moreover, this kind of system is well-suited for hunting new threats. With this solution, you minimize or completely prevent the following effects: financial losses, reputational damage, operational disruptions caused by malware — and regulatory fines under frameworks like NIS2.

Key features (No comparable solution with these features can be found through search engines):

HEX DEREF X (Endpoint Security | Anti-malware) is a standalone enterprise security product that combines proactive detection and response (EDR) capabilities with application- and process-level Zero Trust enforcement (allowlisting). This unique combination enables both threat prevention and deep system visibility within a single platform. Unlike standalone monitoring and analysis tools, the solution integrates key operational capabilities comparable to ProcMon64 and System Informer directly into the security product itself, eliminating the need for multiple separate tools.
  • Competes easily with enterprise-grade solutions such as CrowdStrike Falcon Enterprise by providing comprehensive kernel-level visibility into Windows systems
  • https://www.crowdstrike.com/en-us/pricing/falcon-pro/ — https://assets.crowdstrike.com/is/content/crowdstrikeinc/falcon-endpoint-protection-pro-data-sheetpdf — CrowdStrike Falcon Pro keeps detection details for 90 days, but not the full raw process, command-line, registry, and network telemetry unless the customer enables FDR (Falcon Data Replicator).
  • It can easily compete with ESET Elite Protection. Based on their pricing, this solution could be marketed at a similar price point — https://www.eset.com/us/business/elite-protection/
https://www.welivesecurity.com/en/eset-research/romcom-exploits-firefox-and-windows-zero-days-in-the-wild/
The solution helps expose these types of attacks at a much earlier stage. A zero-day attack like this can lead to the compromise of virtually any organization. Even when the underlying vulnerability is completely unknown, the resulting processes, command-line activity, network connections, and other system-level events remain available for investigation. This enables threat hunters to obtain a comprehensive view of suspicious activity through a single interface. Security awareness training alone is not sufficient to defend against browser-based zero-day attacks because victims may be compromised without warning and, in some cases, without any meaningful user interaction.
https://www.microsoft.com/en-us/security/blog/2026/08/04/129-seconds-disruption-microsoft-defender-stops-ransomware-qnet/
HEX DEREF X - Endpoint Security disrupts sophisticated multi-stage attacks by combining behavioral detection, kernel-level visibility, and application-level Zero Trust enforcement. In the RomCom attack chain, the product can identify the browser-spawned PowerShell execution, expose/prevent privilege escalation activity in near real time, and prevent the downloaded second-stage DLL payload from executing unless it is explicitly trusted. As a result, the attack can be contained before meaningful compromise of the endpoint occurs.


  • Full access to process command-line and network telemetry, without vendor-imposed retention limits
  • Threat hunting
  • Early attack chain disruption
  • Prevent ransomware attacks and data breaches before they even have a chance to begin—even when the threat originates from within the organization
  • Zero Trust - In this security-enhanced mode, the system implements strict execution controls that block all code from running without the user’s deliberate initiation or explicit consent (excluding Microsoft-digitally-signed processes). Everything else is blocked by default and flagged as an anomaly for manual analysis. Not even an APT-level ransomware or spyware can cause any damage. Although a process or its digital signature may be whitelisted, its behavior is continuously monitored to detect any potential malicious activity that may emerge over time
  • Advanced process protection: Processes can be protected at the kernel level based on their digital signature, ensuring: Process memory cannot be read or written from user space. Protected processes are immune to code injection. By configuring the settings, browser processes can be secured in such a way that even fileless malware cannot hide within them. Most importantly, it prevents the extraction of user credentials or other sensitive information from browser memory
  • The attack surface is minimized to a near-zero level
  • Anomaly detection flags any deviation. Zero-day threats are neutralized before they can act — because they’re not on the allowlist
  • Advanced malware analysis and memory forensics
  • Designed to accelerate root cause analysis, the solution enables rapid identification and resolution of system anomalies, minimizing downtime and enhancing operational resilience
  • Kernel physical memory scanner
  • User-mode memory scanner, including WinTcb protected processes
  • Secure IOCTL communication (The Exploitation #1 and Exploitation #2 mentioned in the article is not possible with this protection)
  • A Next Generation Anti-Virus (NGAV) goes beyond traditional antivirus solutions – no signature updates, no reboots, and operates seamlessly even offline
  • The solution runs alongside existing endpoint protections and kernel-level anti-cheats, while also providing deep visibility into their behavior
  • Proactive nature - After detecting an anomaly, it can automatically capture a memory dump from kernel memory or user-space memory based on predefined actions or isolate the device from the network where the anomaly was detected. This enables an immediate forensic analysis without requiring on-site teams
  • Always-on, real-time defense at the kernel level because threats never sleep
  • Protected Folders (ransomware and data theft protection)
  • Protected Folders (ransomware and data theft protection)
  • Detects privilege escalation

The solution logs all processes along with their command lines and network connections into the database. This supports the investigation of potential data breaches and malware analysis.

In the solution's Zero Trust mode, the attack surface shrinks to almost nothing, and all processes that are not added to the allowed list (excluding those signed by Microsoft) are blocked at the kernel level in real time. This ensures that even a previously undetecteded most sophisticated malware cannot inflict any damage.

The allowed applications list is maintained by the device user. This can be tailored through software development to suit your organization’s requirements.

The user interface (UI) has been coded with C# .NET 8.0 so that the project would be easier to customize and be more easily modifiable.

This solution does not require or use any third-party additional protection layers. Therefore, the kernel driver is stable, and the source code is maintainable and well-documented.

Advanced memory scanner

Detects and exposes all processes (including WinTcb protected) accessing user credentials in real time. Instantly flags any activity involving the exfiltration of sensitive data. You'll be astonished by what it uncovers — threats you didn't even know existed.

Unauthorized credential access by antivirus or endpoint protection software or kernel-level anti-cheat? This solution ensures it's detected — no exceptions. No search engine reveals a memory scanner like this — there’s nothing remotely similar to compare results with.
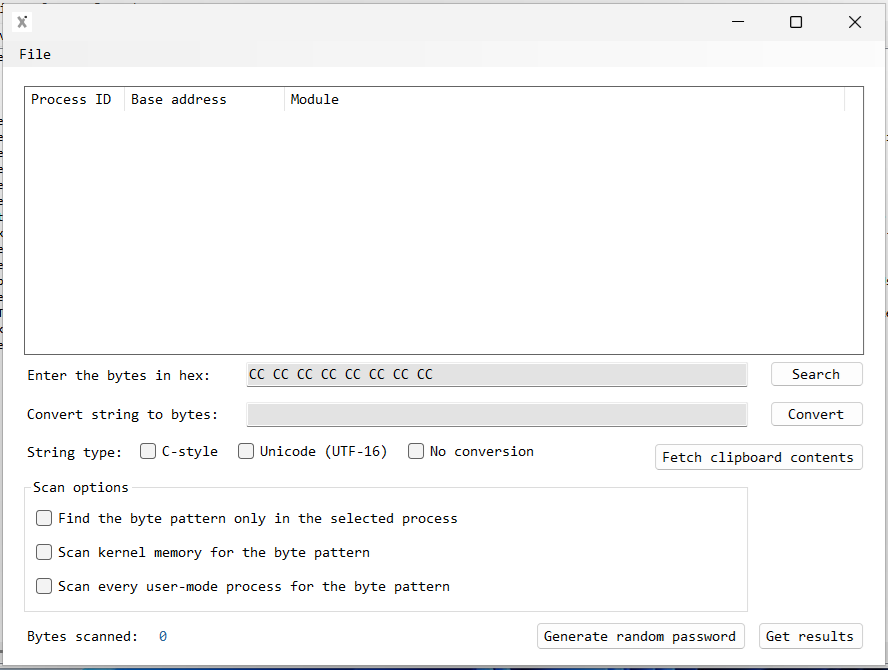
HEX DEREF X - Advanced memory scanner

Availability of the source code

The user interface (UI) is written in C# .NET 8.0. The kernel driver is written in C/C++. Total transparency: Review, audit, and adapt the code to meet your security standards. Brand freedom: Deploy under your own company name and visual identity. The original author offers a cybersecurity solution built on the principle that real trust begins with visibility. The source code:
  • Can be licensed on a non-exclusive basis for internal corporate use
  • Is sold as commercial software development work on a non-exclusive basis, as-is at the time of purchase
  • Provides a solid foundation for developing kernel-level anti-cheat mechanisms on Windows with relative ease
The source code includes, among other features:
  • A process monitoring driver
  • A file-system filter driver
  • A registry filter driver
  • A handle monitoring driver
When you deploy a closed-source EDR product or a similar security solution within your organization, you are placing a significant amount of trust in the vendor ( https://overlayhack.com/unknown-malware-threat#privacy ), as such software typically has extensive visibility and privileged access to the endpoint. From a security perspective, a compromised or malicious vendor could effectively turn that software into a Trojan horse on your devices. Access to the source code enables full SOC integration. Most importantly, it ensures that critical telemetry remains within the telecom operator's own network. When the collection of process command-line data and network connection telemetry is not restricted, threat hunting for unknown malware is not limited by the vendor, and security teams can conduct far more effective post-incident and breach investigations.
The origin of the source code must not be misrepresented. The original author of the source code is White Byte. The logo is the copyrighted creation of the original author and may not be used in any rebranded or derivative solutions without explicit permission.

Investors

Zero Trust

No team, no budget, just one developer, White Byte , turning zero into something remarkable.
HEX DEREF X Endpoint Security provides both proactive NGAV detection and response capabilities and an optional application- and process-level Zero Trust enforcement mode. In its standard configuration, the platform continuously monitors, detects, and responds to threats while delivering deep visibility into system activity. When Zero Trust mode is enabled, it shifts from detection and response (EDR) to prevention-first, stopping unauthorized behavior before it can result in a compromise. Malware either fails to execute effectively or is exposed immediately. The platform also features unlimited logging of process command-line activity and network connection telemetry to a local database. These capabilities can be disabled by the user at any time. HEX DEREF X is designed with privacy in mind and does not transmit sensitive information without the user's explicit consent.
Based on my market research, most antivirus and endpoint security products provide little or no visibility into critical security telemetry. Process command-line activity and associated network connections are often hidden from end users, despite being among the most valuable data sources for threat detection and incident investigation.
In a way, the traditional antivirus approach has failed its users by losing sight of its original purpose. Rather than showing users what is actually happening on their systems, many products collect sensitive information in the background without first obtaining the user's explicit consent.
Key Value Proposition:
  • Combines multiple critical malware analysis tools into a single product
  • Performs all operations at the kernel level (including a custom driver)
  • High compatibility with the broader analysis-tool ecosystem
  • No direct competitor; the closest comparison is System Informer, but HEX DEREF X provides broader functionality and deeper kernel-level integration
https://www.welivesecurity.com/en/eset-research/romcom-exploits-firefox-and-windows-zero-days-in-the-wild/
HEX DEREF X’s application- and process-level Zero Trust mode not only blocks this type of attack but may also reveal previously undetected zero-day vulnerabilities in non-browser processes.
Why choose HEX DEREF X Endpoint Security for critical infrastructure? It operates even in fully isolated environments without an internet connection.
For critical infrastructure operators, visibility, control, and independence are fundamental cybersecurity requirements. The source code available with HEX DEREF X Endpoint Security enables independent auditing, technical evaluation, and custom integrations tailored to an organization's specific operational and security requirements.
From a NIS2 compliance perspective, a key advantage is that critical telemetry can be processed and retained entirely within the organization's own environment. This reduces dependence on external services and helps ensure that security-critical data remains under the organization's direct control.
The initial reaction was essentially along the lines of: "We don't trust random vendors." Such an approach does little to promote innovation and instead favors established players regardless of technical merit. This can create an environment where superior technologies are overlooked simply because they originate from less well-known vendors.
With closed-source security products, customers must ultimately trust the vendor's implementation and data-handling practices. Source code availability provides transparency, enables independent verification of product behavior, and supports long-term risk management, particularly in critical infrastructure environments.
HEX DEREF X can be integrated with existing SOC, SIEM, and monitoring solutions while keeping security telemetry within the organization's own network and operational control.
https://www.microsoft.com/en-us/security/blog/2026/08/04/129-seconds-disruption-microsoft-defender-stops-ransomware-qnet/
https://therecord.media/chinese-apt-targeted-exchange-servers-with-four-zero-days-microsoft-says
Without a Zero Trust security model, an EDR or endpoint security solution cannot reliably determine which code should be trusted by default.
Ultimately, the most important capability is the ability to detect and prevent new and previously unknown cyberattacks, particularly those leveraging zero-day vulnerabilities, before they can cause operational or financial damage.
Through access to the source code, telecommunications operators can achieve a significant degree of self-sufficiency in Windows platform security while maintaining control over the future evolution of the solution according to their own business requirements.
At the same time, they can establish a meaningful competitive advantage in the market, especially where competing providers are unable to offer an equivalent level of transparency, control, and customization.
Target Market:

If a telecom operator acquired the HEX DEREF X: Endpoint Security source code through a non-exclusive software-development agreement, it would retain 100% of the revenue generated by the solution while reducing its reliance on third-party cybersecurity vendors. Instead of paying external vendors for endpoint security capabilities, the operator could offer its own proactive security service directly to customers. The commercial opportunity extends beyond enterprise customers. Many consumers would likely be willing to pay an additional fee as part of their mobile subscription for a proactive security solution that delivers capabilities not commonly available even in many enterprise-grade endpoint security products. This would allow operators such as Elisa, Telia, or DNA to improve cybersecurity, strengthen customer loyalty, differentiate their services from competitors, and create a new recurring revenue stream. A telecom operator could also act as a reseller for its business customers.

  • Cyber Security Analyst
  • SOC Analysts
  • Malware Analysts
  • Security Researchers
  • Security Engineers
  • Reverse Engineers
  • Threat Hunters
  • Red team / blue team professionals
  • IDA PRO users
  • Security laboratories and SOC teams
  • Cybersecurity companies requiring deep analysis and kernel-level visibility
Commercialization Status
The product is ready for release but requires:
  • An EV code-signing certificate
  • A registered company to obtain the certificate
  • Potential funding for finalization, marketing, and documentation

An EV code-signing certificate is required to register an organization with Microsoft's Hardware Developer Program and to establish its identity within the Hardware Partner Center. The certificate is associated with the organization's Partner Center account and is a prerequisite for submitting kernel-mode drivers for Microsoft signing. In that sense, the EV certificate effectively serves as an organizational identity credential for accessing Microsoft's hardware signing infrastructure. The certificate itself does not necessarily have to be used to sign the driver submitted to Microsoft, although Microsoft recommends using an EV certificate for individual submissions.

Why Invest:
An architecturally distinct endpoint security platform designed to address limitations commonly found in traditional EDR and antivirus solutions for Windows environments. This is particularly evident in the enterprise endpoint security market, where U.S. vendors dominate. A contributing factor is that much of the expertise and innovation has migrated abroad because Finland has not produced products that are competitive enough on a global scale.
The remaining requirements are simply an EV code-signing certificate and an established company. Hex-Rays reseller network ( https://hex-rays.com/partners ) could be a valuable channel for reaching international markets. The product has substantial market potential, as there appears to be no direct competing solution offering the same combination of capabilities.
HEX DEREF X directly competes with CrowdStrike Falcon, providing comprehensive endpoint security and deep Windows kernel-level visibility. https://www.crowdstrike.com/en-us/products/trials/try-falcon/
The product's value is built on highly specialized technical expertise that is difficult to replicate, rather than relying primarily on marketing, user experience, or business model innovation. As a result, competitors face significant barriers to developing an equivalent solution in a short period of time.
It is also worth considering the current state of Finland's cybersecurity ecosystem. Without continued investment in the development of new domestic cybersecurity technologies, both strategic expertise and future industry investment may gradually move elsewhere. Over time, critical kernel-level engineering expertise risks being lost.
Today, many of Finland's largest telecommunications operators rely on endpoint security solutions developed outside Finland. This means that both economic value and advanced cybersecurity expertise increasingly flow abroad.
HEX DEREF X presents an opportunity to help reverse this trend by providing a domestically developed, technically competitive security platform that helps retain expertise, innovation, and value within Finland.
  • A unique product with no direct competitor
  • High market potential as cybersecurity demand grows
  • Deep technology ideal for early-stage VC investors — the product is based on rare, technically demanding expertise that is difficult to replicate and provides a clear competitive advantage
  • A functional minimum viable product (MVP) already exists
  • Opportunity to build a company that offers endpoint protection, malware analysis tools, and kernel-level anti-cheat technology through a single unified Windows platform
  • As a byproduct of the Anti-malware implementation, I also have an in-development kernel-level anti-cheat system (core functionality implemented and tested) HEX DEREF X - ANTI-CHEAT

The United States June 2024 ban on the sale and distribution of Kaspersky cybersecurity products highlighted a broader strategic issue: endpoint security solutions operate with highly privileged access and have visibility into virtually all activity occurring on an endpoint. As a result, trust in the vendor and the organization behind the product becomes a critical component of the overall risk profile.

Simply auditing third-party software does not, by itself, solve this challenge. A more meaningful long-term strategy would be to develop domestic expertise and technology. The HEX DEREF X source code could provide a foundation for a Finnish-developed endpoint security solution, malware analysis platform, and a Windows kernel-level anti-cheat technology capable of competing easily with established international products such as Easy Anti-Cheat and BattlEye.

Despite all the efforts (as of 10/2026, 5+ years of constant development by the author), the solution is a work in progress (WiP).

ABOUT AUTHOR

I am self-taught coder (a total of 16 years of coding experience as of 06/2026 in PHP/C#/C/C++). The original author does not hold a bachelor's degree in cybersecurity but that does not mean that I am not capable. I am also a hobbyist Windows internals researcher and reverse engineer. A work of mine: DSE/PatchGuard bypass at runtime Windows 10 22H2 PRO - Windows 11 25H2 PRO I coded overlayhack.com in PHP back in 2012 and later improved the codes 2018 and designed it's MySql database. My motto is. If I need to get something done. I will just do it and I am usually very good at what I do.